Quick answer
To install an APK safely, get it from Google Play or the developer's own site, allow Install unknown apps for one app only, and match the signer certificate before you tap Install. As of October 2026, Android's developer verification has covered only participating stores in four countries since September 30, 2026, with a global rollout planned for 2027. Start with the source, then the signer check.
You searched for Eduuolvera because an app you want isn't in your Play Store, or a friend sent an APK link. An APK is the package file Android uses to install an app. A site that lists APKs from many developers is a mirror, and we couldn't confirm who runs this one, so we don't link it.
We start with whether APK mirror sites are safe and where an Android app should come from. Then we cover the one-app permission, what Play Protect checks, and the signer certificate check, with our own local test. We finish with developer verification in 2026 and what to do if a bad APK already got through.
Key takeaways
- Download an APK only from Google Play or the developer's own site.
- Allow Install unknown apps for one app, then switch it off.
- Keep Play Protect on, since it also scans apps from other sources.
- A matching SHA-256 signer fingerprint shows which key signed the file.
- Our impostor certificate copied the developer name, not the fingerprint.
Is it safe to download an APK from a site like Eduuolvera?
It depends on the signer. A mirror page can't show you who that is. Android's app signing overview says apps "can be signed by a third-party (OEM, operator, alternative market) or self-signed." It also says "Android currently doesn't perform CA verification for app certificates," so no outside authority vouches for the name inside a certificate.
The signature still does real work. Android's signing guide says "Android requires that all APKs be digitally signed with a certificate before they are installed on a device or updated." The overview adds that signing is "the first step to placing an app in its Application Sandbox," which keeps one app from reading another's data.
But a signature only proves which key signed the file. Anyone can make a key and type a famous company's name into it. Our test below tries it with a made-up name.
Government guidance points the same way. CISA's archived page on malicious code, last revised in 2019, warns that "It is not uncommon that free software contains a Trojan horse." Such a program looks legitimate while it does harm. The FTC's malware guide says "Don’t use unfamiliar websites to download free stuff like music, movies, shows, or games." Paid apps offered free on a mirror fit that warning, and so do modded games that promise unlocked features or unlimited coins.
Where an Android app should come from
So the first decision is the source. Android's developer docs cover app marketplaces, a developer's website and email. Google Play is the default, and the alternative distribution guide calls it trusted. It describes a second route: a developer can "host the release-ready APK files on your website and provide users with a download link."
That second route is the one to look for when an app isn't on Play, such as a beta build or an in-house tool your company hands out. Type the developer's address yourself rather than arriving through a search ad or a forum post, because the FTC's malware guide warns, "Don't click on ads to download software." Lookalike domains are common too, as our lookalike website check shows. The FTC adds "Don’t download content through peer-to-peer (P2P) file-sharing sites," and that covers APKs traded on torrent pages. If the developer publishes a SHA-256 fingerprint for its signing certificate, copy it down for the signer check later.
Here's how the usual sources compare on the two things you can check, the signer and the scan:
| Where the APK comes from | Who signed it | Play Protect scan | What we would do |
| Google Play | Google, with the developer's key (Play App Signing) | Checked before you download | Install from Play |
| Developer's own site | The developer | Checked on your phone at install | Match the published fingerprint first |
| A file sent by email or chat | Unknown until you check | Checked on your phone at install | Ask the sender for the developer site |
| A mirror or APK listing site | Unknown until you check | Checked on your phone at install | Skip it unless the fingerprint matches |
A mirror can host the developer's real file, but only a fingerprint from the developer can prove it. Email delivery is weak too, since the guide says sending APKs that way "provides few protections from piracy and unauthorized distribution."
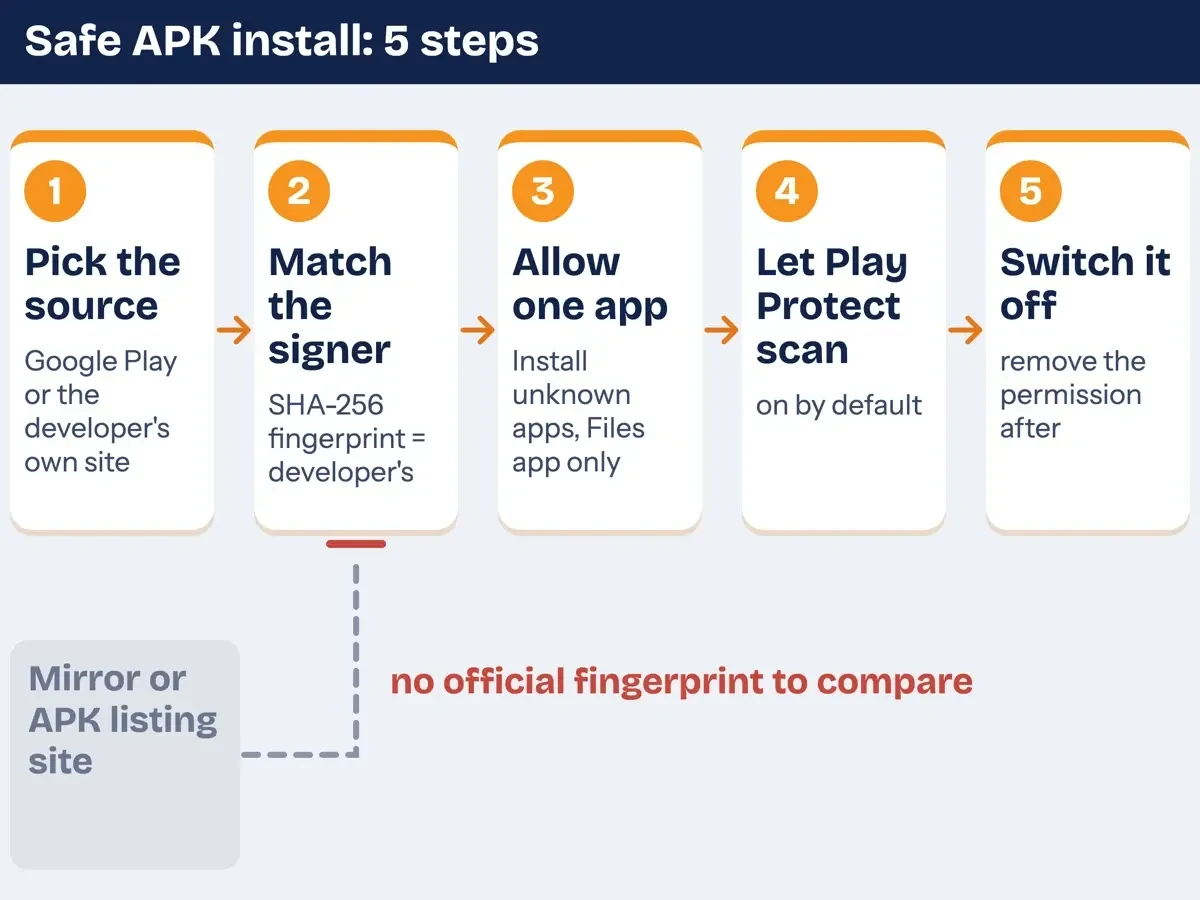 Diagram by DigitalTreed, from Android Developers and Google Play Help pages read October 30, 2026.
Allow one app to install, then switch it off
Once you've got the file from a source you trust, Android still blocks the install. The same Android guide says "Android blocks such installs until the user opts into allowing the installation of apps from other sources." On Android 8.0 and higher, that switch sits on a settings screen called Install unknown apps. It's per app, not phone-wide. The guide says that screen is where you "enable app installations from a particular location," such as your Files app or one browser. Android's Settings reference describes it as settings "to allow configuration of trusted external sources," and apps can open it for one named package. Menu paths differ by phone maker, so search Settings for the screen's name.
- Pick the one app that will open the APK, usually your Files app.
- Open Install unknown apps in Settings and allow that app only.
- Open the APK from that app and read the install screen before you confirm.
- Go back to Install unknown apps and switch that app off again.
The last step is our habit, not an Android rule. On Android 7.1.1 and lower there's a single Unknown sources switch under Settings > Security instead. For those phones the guide advises that "users should allow only one unknown app installation at a time if the option is available to them." A browser left on the list lets any page that pushes an APK reach your install screen, which is why we'd never leave one there. The guide also warns that "Some network providers don’t allow users to install applications from unknown sources," so a carrier-managed phone may not offer the switch at all.
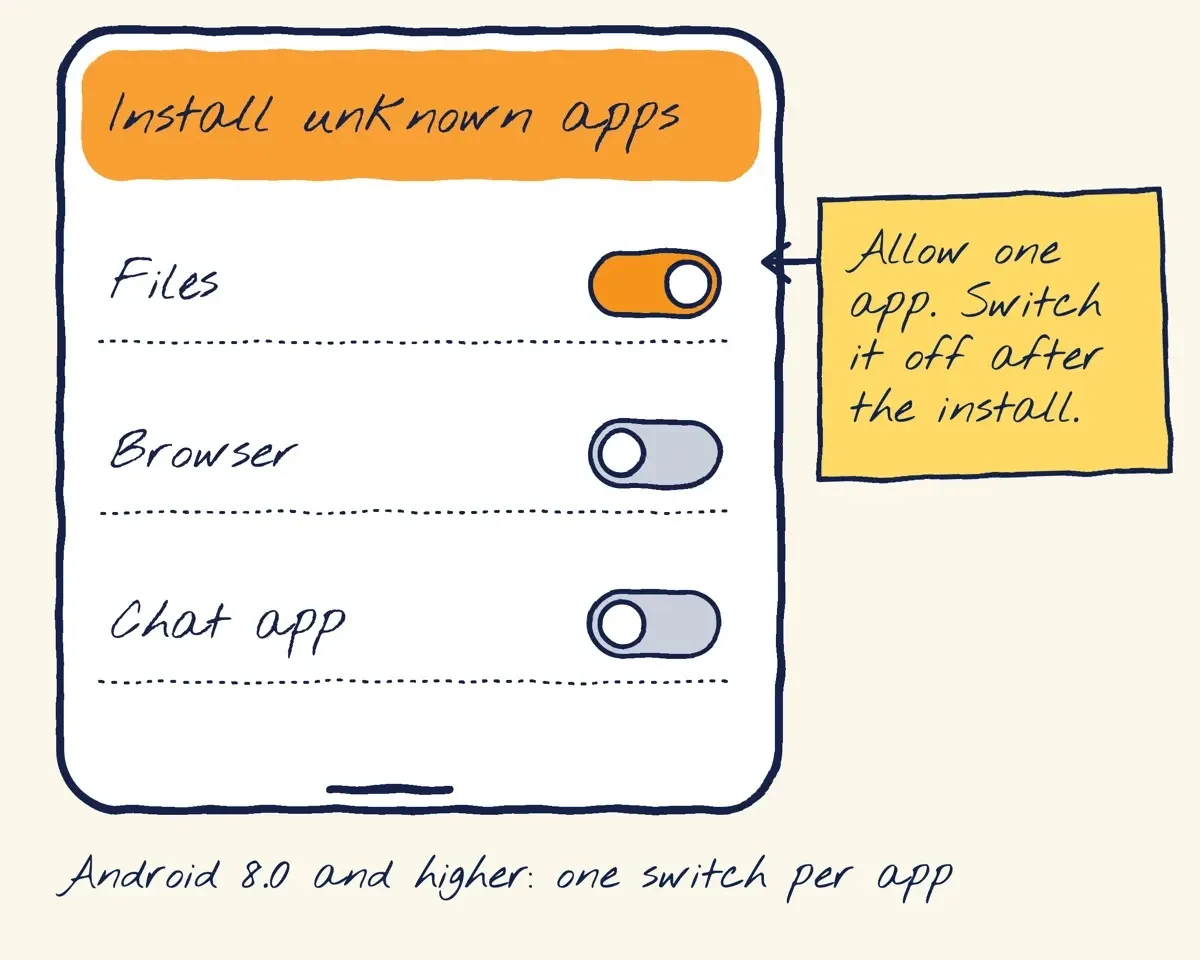 Drawn by us, from the Android Developers guide to installing unknown apps, October 30, 2026. Not a real phone screen.
What Play Protect checks before and after install
That install screen isn't your only check. Play Protect looks at sideloaded apps too. The Google Play Help page on Play Protect says it "checks your device for potentially harmful apps from other sources." It's on by default, and Google says to "always keep Google Play Protect on."
Checking it takes a minute in the Play Store app. Google Play Help gives these taps:
- Open the Google Play Store app and tap your profile icon at the top right.
- Open Play Protect, then its settings, and check that Scan apps with Play Protect is on.
- For your phone's certification, tap the profile icon again, then Settings, then About, and look for Play Protect certified.
If the Play Store reports "Device is not certified," Google Play Help says not to troubleshoot Play Protect and points you to its Fix device issue button.
For an app Google hasn't seen, the scan goes deeper. The Android Help copy of the page says you may be asked to scan an app from outside Play. It adds that "Scanning the app will send app details to Google for a code-level evaluation." Play Protect may also block an install that "is unverified and uses sensitive device permissions that are commonly targeted by scammers to commit financial fraud." Google's Play Protect page for developers puts the scale at "200 billion Android apps daily." That's Google's own figure. We found no second source. A clean scan lowers the risk, but it can't tell you whether the file came from the developer you meant to trust.
Check the signer certificate before you tap Install
That's the question the signer check answers. Android's apksigner tool ships in Android SDK Build Tools revision 24.0.3 and higher. Its verify command takes a --print-certs option that will "Show information about the APK's signing certificates." You compare the certificate details it prints, including the SHA-256 value, with the fingerprint the developer publishes on its own site.
apksigner verify --print-certs app.apk
# compare the printed SHA-256 value
# with the fingerprint the developer publishes
It runs on a computer. Our Android Studio on Ubuntu guide covers getting the SDK. The tool also catches edits, and its page warns that "If you sign your APK using apksigner and make further changes to the APK, the APK's signature is invalidated." The signing overview says "Any modification to the APK, including ZIP metadata modifications, invalidates the APK signature" under the v2 and newer schemes.
Updates are where a wrong signer bites later. The signing guide says an installing update "compares the certificate(s) in the new version with those in the existing version." Then "The system allows the update if the certificates match." If a developer signs with a different certificate, the guide says "the user installs the new version as a completely new app." So a mirror copy signed with another key can't take the real developer's updates, and switching back means uninstalling it.
Where does the right fingerprint come from? The signing guide calls a certificate fingerprint "a short and unique representation of a certificate," and developers see the MD5, SHA-1 and SHA-256 fingerprints in Play Console. That certificate is "intended to be shared, as it does not contain your private key," the guide adds. If the developer's site doesn't publish the fingerprint, ask its support address for it before you install.
On old phones, the signing overview says "Older Android platforms ignore v2+ signatures and thus need apps to contain v1 signatures." It also says "v1 signatures don't protect some parts of the APK, such as ZIP metadata." That's why apksigner is worth running even for an old phone. Its page says the tool checks that a signature "will be verified successfully on all versions of the Android platform supported by that APK."
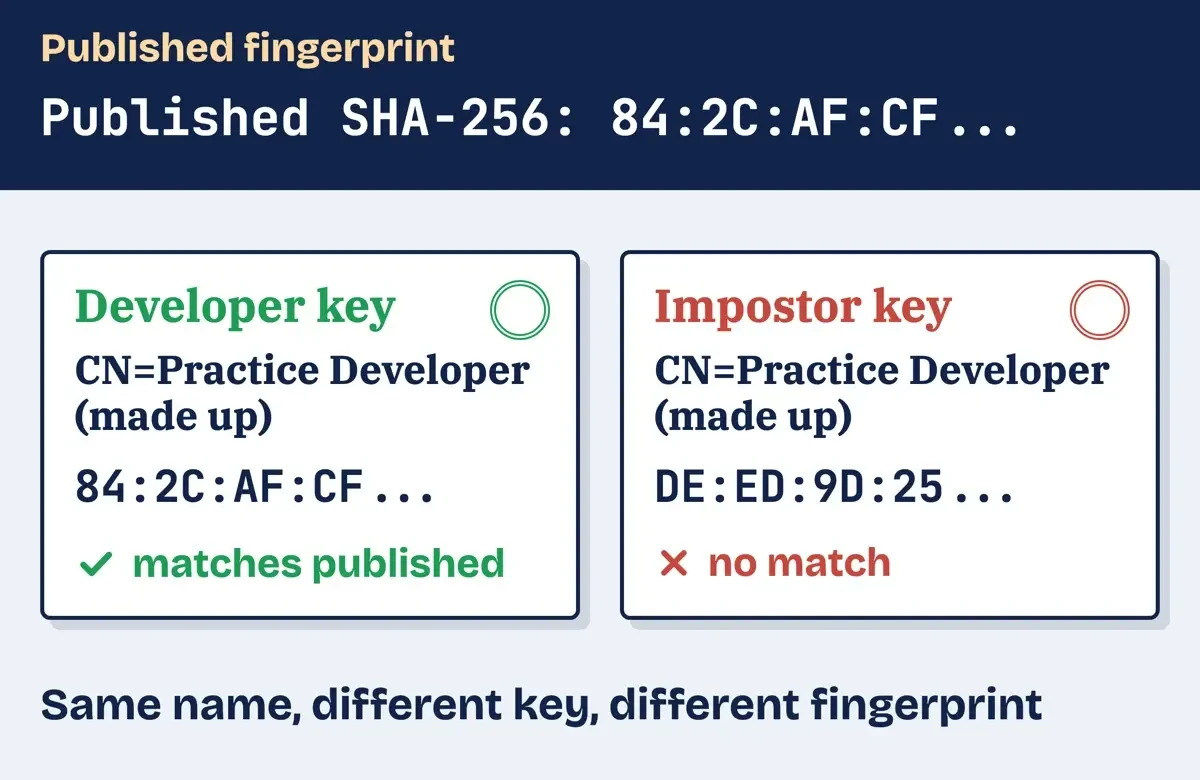 Diagram by DigitalTreed, from our local openssl test results, October 30, 2026.
What we tested
The apksigner tool isn't on our test Mac, and keytool there is only a stub without Java. So on October 30, 2026, a script made two self-signed openssl certificates with one made-up name. It signed a 170-byte practice ZIP with each, then changed one letter in a copy. No APK was downloaded.
same name: CN=Practice Developer (made up)
fingerprints: 84:2C:AF:CF... vs DE:ED:9D:25...
hash: 549c0046... published, 816ba42a... tampered
A developer signature: Verification successful
B tampered file: content verify error
C impostor signature: certificate verify error
Same name, different fingerprints: 84:2C:AF:CF and DE:ED:9D:25. The changed byte broke the hash and the developer's signature. The impostor's signature failed because openssl trusted only the developer's certificate. This isn't Android verification or apksigner output, just the fingerprint idea.
Developer verification changes sideloading from 2026
Google is adding a check on the developer behind each app, too. Its developer verification page says protections began September 30, 2026, for users installing "from participating stores in Brazil, Indonesia, Singapore, and Thailand on certified devices running Android 7+." It says verification "will be expanded globally for all apps on certified Android devices in 2027." A US phone isn't in that first group. The Android Developers Blog post from June 2026 lists an "advanced flow for installing apps from unverified developers" with "security checkpoints to resist coercion scams." In the four launch countries, it says unregistered apps "can be sideloaded with Android Debug Bridge (adb) or advanced flow."
Play developers are mostly covered already, since Google's verification overview says "Google Play automatically registers 99% of apps."
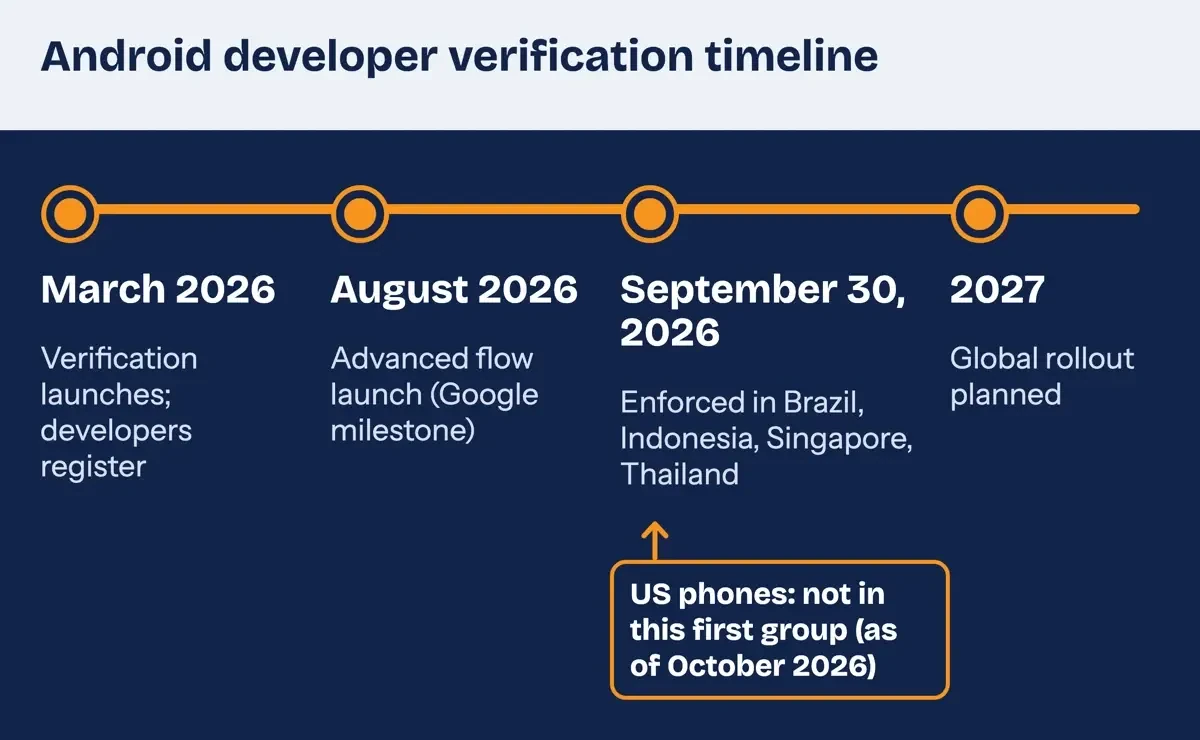 Diagram by DigitalTreed, from Android Developers pages read October 30, 2026.
If a bad APK already got through
Installed something already? Start with Play Protect. The Play Protect help page says a flagged app may trigger a notification, be disabled "until you uninstall it," or be removed automatically. To remove it yourself, tap the notification, then Uninstall. Next, close the door it came through by switching off every app on Install unknown apps that you don't use for installs. Then patch the phone. The FTC's phone security page says "Set your phone to update automatically" and "Update your apps, too." CISA's archived update tips say "many software updates are created to fix security risks." CISA's malicious code page also suggests a manual scan of files from "web downloads" if your security app doesn't scan them on its own.
Last, change passwords for accounts you used inside that app, from a clean device. Our phishing-link checklist covers phones.
If the app is gone but the phone still drains fast, our guide to stopping background apps on Android shows where Settings lists what keeps running. On company phones, an installer left switched on is one of the common malware entry points to audit.
Our take: people skip the fingerprint check. It's the only step that ties the file to a developer. If the developer publishes no fingerprint and its support team won't give you one, we'd wait for a Play release rather than install a copy whose signer nobody can confirm. Our tips to avoid phishing help with the links that send people to APK sites in the first place.
APK install questions
Frequently asked
Does Play Protect send my apps to Google?
Only if you allow it. The Play Protect page says "Improve harmful app detection" lets it "automatically send unknown apps to Google."
Can a developer sign an app without a certificate authority?
Yes. Android's signing overview says "Apps don't have to be signed by a central authority."
What happens to permissions for apps I rarely use?
On Android 6.0 to 10, Google Play Help says Play Protect may reset them after 3 months unused.
Can students share an app without verification fees?
Yes. The verification page describes accounts for sharing with up to 20 devices without a fee.
How we made this guide: Android, Google, CISA and FTC pages were saved on October 30, 2026, and a script matched every quote. The signer test used openssl on a made-up file. Facts checked by the DigitalTreed team on October 30, 2026.
First published December 2023 as a review of an APK download site. Rewritten October 30, 2026: the site review and its download steps are gone. In their place are Android's own install, Play Protect and signer checks, plus a local test of the fingerprint method.
Sources
- Android Developers: Alternative distribution options
- Android Developers: Settings reference (ACTION_MANAGE_UNKNOWN_APP_SOURCES)
- Android Developers: Sign your app
- Android Developers: apksigner
- Android Open Source Project: Application signing
- Android Developers: Android developer verification
- Android Developers Blog: Android developer verification, June 2026
- Android Developers Blog: Android developer verification rolling out to all developers, March 2026
- Google Play Help: Use Google Play Protect to help keep your apps safe
- Android Help: Use Google Play Protect to help keep your apps safe
- Google for Developers: Google Play Protect
- CISA: Protecting Against Malicious Code (archived)
- CISA Secure Our World: Update Software (archived)
- FTC: Malware: How To Protect Against, Detect, and Remove It
- FTC: How To Protect Your Phone From Hackers
Comments
No comments yet. Start the conversation below.