
Quick answer
No public record confirms a Thejavasea.me AIO-TLP breach as of November 11, 2026: 0 of the 5 breach record checks we ran named it. A company breach notice or a state attorney general listing would change that, and none of 5,429 California notices does. If you used the site, change any password you reused there first, then turn on MFA.
If the phrase "Thejavasea.me leaks AIO-TLP" has you worried about an old email address or card number, the public records we checked give a short answer. None of them names it. Thejavasea.me is a domain name registered on March 19, 2022 through Key-Systems GmbH, with its owner hidden behind a privacy service. We'd treat the leak claim as unconfirmed and still lock down your accounts, since a password change and a credit freeze protect you whether or not anything leaked. If a leak has already cost you money, talk to a licensed attorney in your state.
The record table comes first, then what AIO and TLP mean and why we never opened the site or its files. The US steps follow, most urgent first: your own data, passwords and MFA, a credit freeze and IP PIN, and reporting identity theft.
Key takeaways
- None of our 5 breach record checks named Thejavasea.me or AIO-TLP.
- TLP is a real four-label sharing standard, not the name of a leak.
- Change any password you reused on the site before anything else.
- A credit freeze is free by federal law at all three bureaus.
- The IRS online IP PIN tool goes offline from November 16, 2026.
Is the Thejavasea.me AIO-TLP leak confirmed?
A breach becomes a matter of record when the company that lost the data says so, or when a regulator, a court or a breach catalog lists it. On November 11, 2026 none of the five record sets below named Thejavasea.me or AIO-TLP.
| Where we looked | What it covers | Result on November 11, 2026 |
|---|---|---|
| Have I Been Pwned breach catalog | 1,051 breaches, searched by name, title, domain and description | 0 matches |
| California Attorney General breach notices | Organization names in 5,429 notices reported January 20, 2012 to November 9, 2026 | 0 matches |
| Washington Attorney General breach notices | First page of the table only, 48 notices (later pages not read) | 0 matches |
| SEC EDGAR full-text search, "AIO-TLP" | Electronic filings since 2001 | 0 filings |
| SEC EDGAR full-text search, thejavasea | Electronic filings since 2001 | 0 filings |
So the details in the March 2025 text of this page have no source we've found. That text said a breach happened and named the kinds of data taken. It also named four possible ways in, said the data was sold on dark web markets and guessed that AIO means all-in-one. Our test logged six claims from it, and the only one a record supports is that TLP is a real term. There's no record tying even that to this leak, so this rewrite drops the rest. A missing record doesn't prove nothing leaked, since a small site with no US business may never file a notice. It does mean nobody knows what, if anything, was taken.
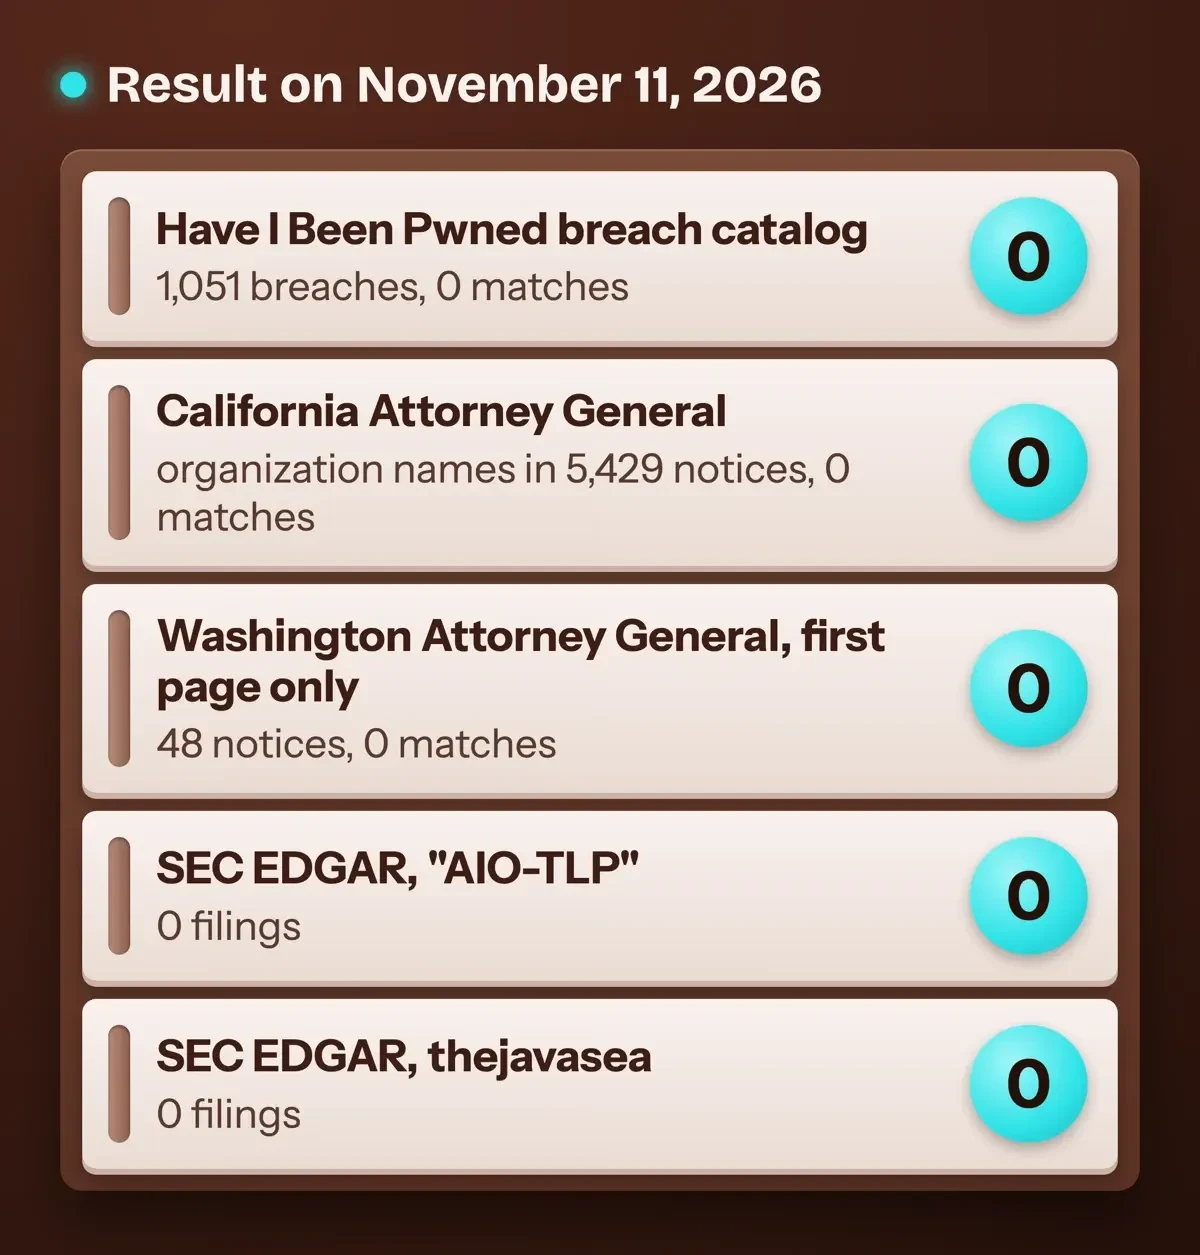 Diagram by DigitalTreed: the five record checks we ran on November 11, 2026 and their results.
What we tested
We ran test/leak_check.py locally on November 11, 2026. It read DNS, WHOIS and RIPE records for the domain, then matched the name against the five record sets above. It didn't contact the site. The name points to an address range registered in Italy, and the registry's expiry date is March 19, 2028.
What AIO and TLP mean, and what they don't prove
The one old claim a record supports holds up: TLP stands for the Traffic Light Protocol, which the incident response group FIRST publishes as a standard. It has four labels: TLP:RED, TLP:AMBER, TLP:GREEN and TLP:CLEAR. FIRST says "Only labels listed in this standard are considered valid by FIRST." TLP:CLEAR means "Recipients can spread this to the world". A label like that tells readers how widely they're allowed to share a security report. It names no leak, site or data set. There's no TLP label called AIO, and FIRST adds that labels "MUST remain in their original form". The AIO part isn't defined in any record we read.
CISA adopted the same FIRST version 2.0 on November 1, 2022, and its TLP definitions page says TLP isn't a control marking or classification scheme.
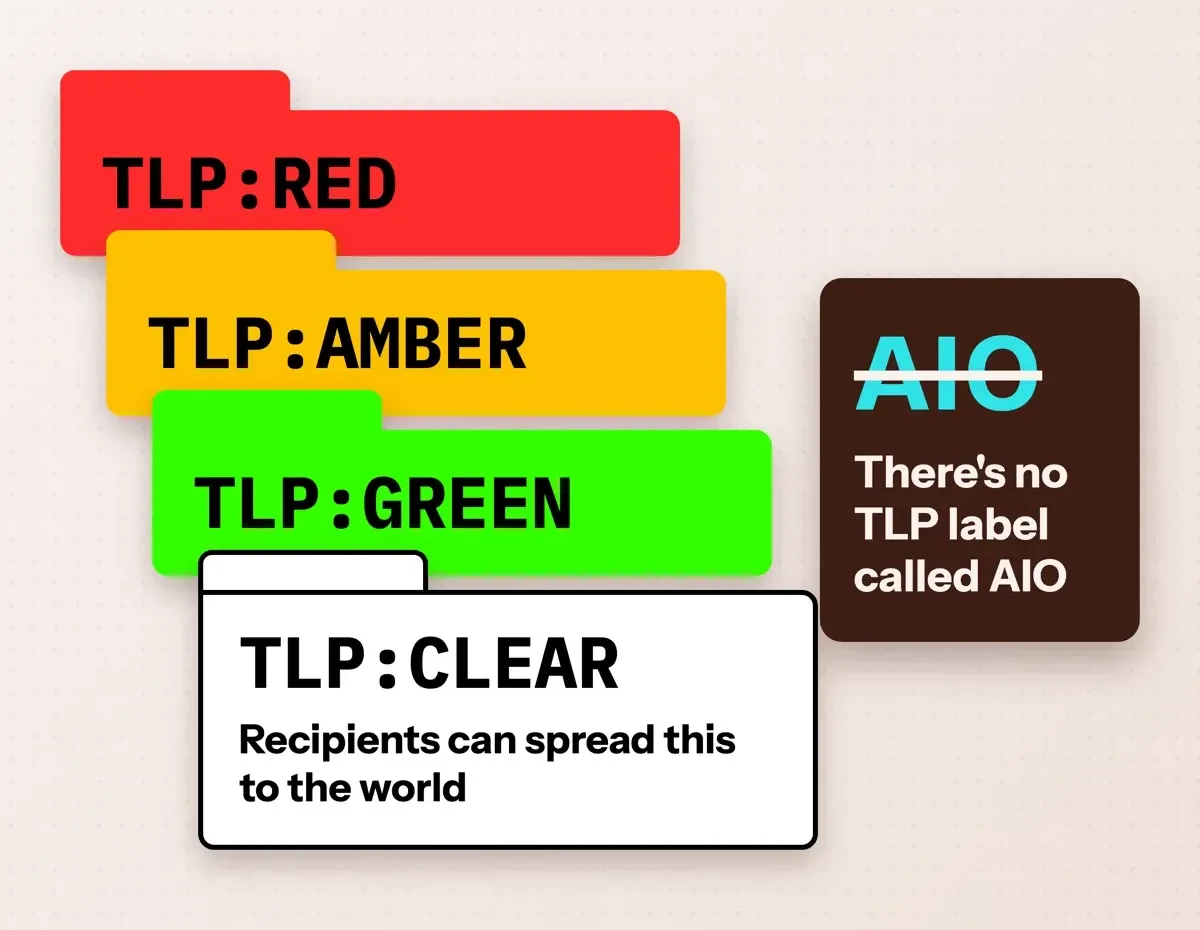 Diagram by DigitalTreed: the four Traffic Light Protocol labels, from the FIRST TLP 2.0 standard.
Have I Been Pwned's FAQ calls files sold under a borrowed name fabricated breaches, where "it is highly unlikely that the breach contains legitimate data sourced from the alleged site". Such files can still "contain actual email addresses" pulled from other leaks. Of the 1,051 breaches in its catalog on November 11, 2026, 3 carry the fabricated flag. Another 42 are marked unverified. So a real email in a file doesn't prove this site was breached; it proves only that the address leaked somewhere.
Why we did not open the site or its files
We never went looking for a file tied to this name. A malware page from the FTC on protecting your devices says "Don't download content through peer-to-peer (P2P) file-sharing sites." A leak sample that's passed around by link fits that warning, and we didn't want a file of unknown origin on a machine that holds our own logins. So we opened none. The pitch arrives by message, too. CISA's phishing page lists "Urgent or emotionally appealing language" and "Requests to send personal and financial information" among the signs. A message that says you're in the AIO-TLP dump and wants you to log in, pay a fee or install a checker shows both signs at once.
If you already clicked one, our steps for a phishing link you already opened cover a PC, a Mac and a phone. Our free antivirus guide for Windows covers the scan, and our phishing prevention tips cover the next fake alert.
Whether opening, keeping or sharing leaked files breaks a law depends on what the files hold and where you live. We didn't find one official page that answers it for every case. A licensed attorney in your state can tell you where you stand before you touch a file.
How to find out if your own data was exposed
If a company did lose your data, start with the records that would name you. In California, a business must notify any resident whose unencrypted personal information was taken, according to the Attorney General's breach list page. It must also send the AG a sample of any notice that went to more than 500 California residents. The AG then posts them publicly. A reported breach that reached more than 500 Californians should show up in that list. Washington runs a similar public list of breach notices. Its table shows how many Washingtonians were affected and what was taken, such as Social Security numbers or bank details.
The FTC's breach response guide for business notes that state breach notification laws set what a notice must say. It lists how the breach happened, what was taken and who to contact. A message that says you're in a leak without those details isn't a breach notice.
For your email address, Have I Been Pwned keeps a public list of breached websites, and on November 11, 2026 it had no entry for thejavasea.me. Your own statements can show misuse that no list will. The FTC's identity theft page says a bill that stops arriving can mean someone changed your billing address, and charges or bank withdrawals you don't recognize are signs too. For an unknown card charge, our walk-through on disputing a charge you do not recognize has the letter.
Change passwords and turn on MFA first
The FTC's two-factor authentication page says scammers buy credentials stolen in data breaches. They try them on the breached site and on any other account that shares the same password. It says to "change your password right away if you find out that your information may have been exposed in a breach." The same page calls that a reason to never reuse the same username and password.
Both agencies start with length. CISA's archived strong password page asks for at least 16 characters, random and unique for each account, kept in a password manager. NIST's SP 800-63B digital identity guidelines set a 15-character minimum for a password used alone. It's eight when the password is one step of MFA.
NIST also tells sites to block "Passwords obtained from previous breach corpuses" and to force a change after a compromise.
Our test/pw_check.py ran those rules over six made-up accounts with made-up passwords. Three accounts shared one 10-character password, and one of them was the made-up forum where a leak was reported. Those three led the change list because one leaked copy opens all of them. Every one of the six got at least one flag. Even the 24-character one lacked MFA. We'd change the email password first in that top group, since your email resets every other password. Then turn on MFA wherever it's offered. CISA's archived MFA page lists a texted code, an authenticator app and a face or fingerprint scan as options. The app makes a new code every 30 seconds.
| Account (made up) | Length | MFA | Flags from our test | Change order |
|---|---|---|---|---|
| 10 | No | under 16 (CISA); under 15 with no MFA (NIST); on blocklist; reused on 3 accounts; same password as the leaked account; no MFA | 1 | |
| Bank | 10 | Yes | under 16 (CISA); on blocklist; reused on 3 accounts; same password as the leaked account | 1 |
| Forum where a leak was reported | 10 | No | under 16 (CISA); under 15 with no MFA (NIST); on blocklist; reused on 3 accounts; same password as the leaked account; no MFA | 1 |
| Work chat | 10 | Yes | under 16 (CISA); on blocklist | 2 |
| Shopping | 16 | No | no MFA | 4 |
| Streaming | 24 | No | no MFA | 4 |
For a password given to a site that promised followers or downloads, our Naz Tricks login theft guide lists the order for social accounts.
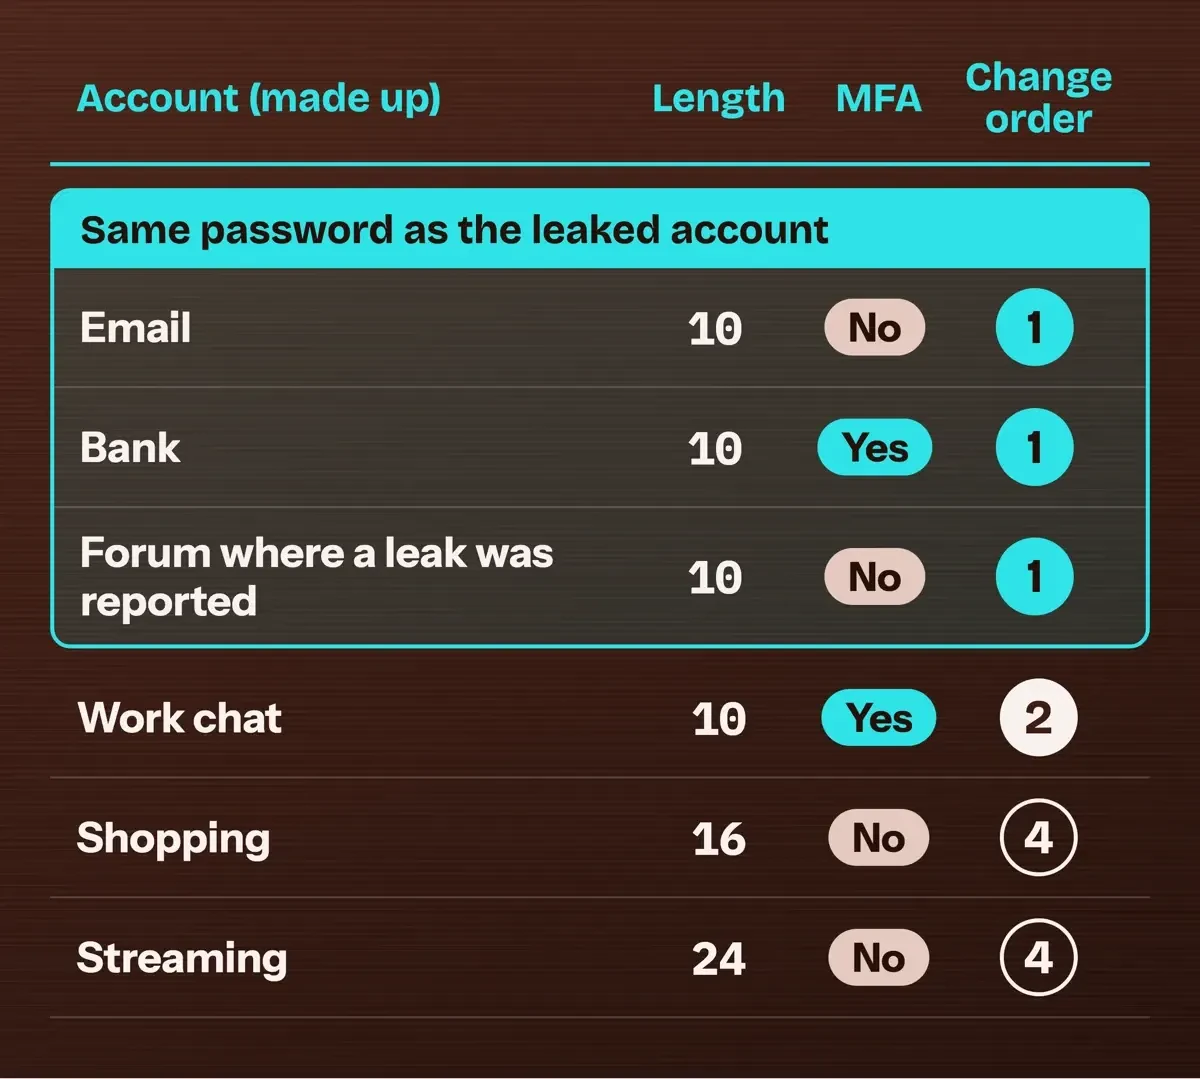 Diagram by DigitalTreed: our password triage on six made-up accounts, from test/pw_check.py run November 11, 2026.
Freeze your credit and protect your SSN
Unlike a password change, a credit freeze guards against new accounts opened in your name. The FTC's credit freeze and fraud alert page says it's free and lasts until you lift it. Creditors on accounts you already hold can still see your file, and you'll contact all three bureaus: Equifax, Experian and TransUnion.
The CFPB's credit freeze answer adds that the bureaus' credit locks often cost money and are "no more effective than security freezes".
Federal law sets the clock. Under 15 U.S.C. 1681c-1, a bureau must place a freeze free of charge within 1 business day of a phone or online request, and lift it within 1 hour. A fraud alert is lighter. An initial alert lasts one year, and you contact just one bureau, which must then tell the other two for you. An extended alert lasts seven years but needs an FTC identity theft report or a police report. We'd freeze rather than rely on an alert. The FTC says that during a freeze "nobody can open a new credit account in your name, including you," while an alert only asks businesses to check with you first.
To watch the accounts you already hold, check your reports. The FTC's free credit reports page says all three bureaus let you check your report once a week for free at AnnualCreditReport.com. Our guide to why free SSN people searches fail covers what else a leaked Social Security number can expose. Tax refunds are a separate target. A credit freeze doesn't cover them. The IRS's IP PIN page calls the Identity Protection PIN "a six-digit number that prevents someone else from filing a tax return using your Social Security number". Anyone with an SSN or ITIN who can verify their identity can get one, even if they don't have to file a return.
Apply before mid-November if you want one. The IRS says its online IP PIN system goes offline for maintenance on Monday, November 16, 2026, and it won't be back until mid-January 2027.
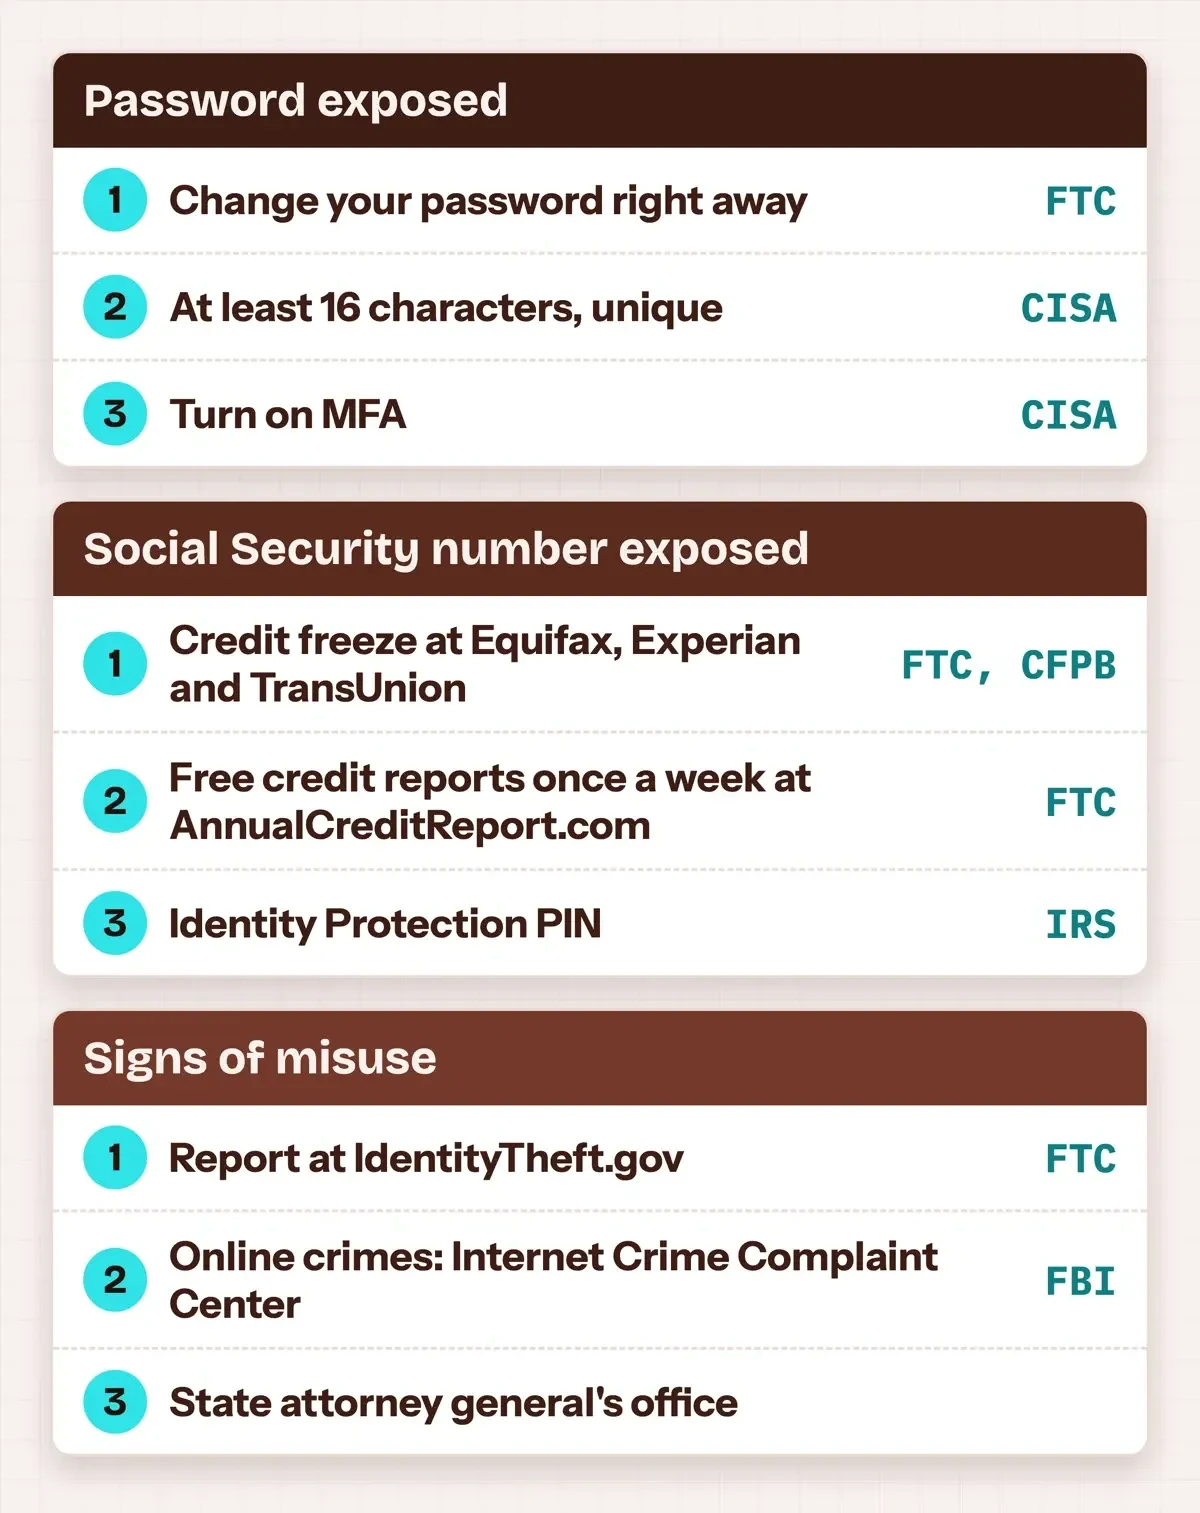 Diagram by DigitalTreed: what to do by the type of data exposed, from FTC, CFPB, CISA, IRS and FBI pages.
Where to report identity theft
Even with a freeze in place, report any sign of misuse in one place first, since the seven-year extended fraud alert needs that FTC report or a police report. The FTC's identity theft page sends you to IdentityTheft.gov, where "You'll get a free personal recovery plan with next steps." You can also report in Spanish at RobodeIdentidad.gov, or call 877-438-4338 and press 3 for another language, with interpreters available from 9:00 a.m. to 5:00 p.m. ET. The FTC's business guide points readers to IdentityTheft.gov/databreach for steps that depend on the type of data exposed.
Online crimes, such as a fake leak checker that's taken your money, go to the FBI's Internet Crime Complaint Center. The IC3 FAQ says complaints "may be referred to federal, state, local or international law enforcement", and its filing terms add "I will not be contacted by the IC3." Your state attorney general's office takes complaints too. A small business whose customer data may sit in a leak has duties that aren't a consumer's. The FTC business guide covers notice letters, and our data protection compliance guide covers the policies behind them. For money lost, a lawsuit or a notice duty you aren't sure about, talk to a licensed attorney in your state.
Frequently asked
Can I check if my email was in the Thejavasea.me leak?
No catalog lists it as of November 11, 2026. Have I Been Pwned's FAQ says it lets people assess where their data has been exposed.
Does a credit lock work like a credit freeze?
Not quite. The CFPB says a freeze is free and a right under law, while locks are often sold for a fee.
When does a fraud alert expire?
After one year for an initial alert. An extended alert lasts seven years and needs an IdentityTheft.gov or police report, per the FTC.
Should I change every password every few months?
No. NIST SP 800-63B tells sites not to force periodic changes, only a change when there is evidence of compromise.
How we made this guide: We saved the 22 pages in Sources on November 11, 2026 and matched each quote in this guide to text in them. The domain was read only through DNS and registry records. Facts checked by the DigitalTreed team on November 11, 2026. We give no legal advice here.
First published March 2025 with claims about stolen data and attack methods that had no source. Rewritten November 11, 2026: dated record checks, what TLP means, and the US steps for a leak.
Sources
- FIRST: Traffic Light Protocol (TLP) version 2.0
- CISA: Traffic Light Protocol (TLP) definitions and usage
- Have I Been Pwned: FAQs
- Have I Been Pwned: Pwned websites
- California Attorney General: Search data security breaches
- Washington Attorney General: Data breach notifications
- SEC: EDGAR full text search
- FTC Consumer Advice: Malware, how to protect against, detect and remove it
- CISA: Recognize and report phishing
- FTC Consumer Advice: Use two-factor authentication to protect your accounts
- CISA: Use strong passwords
- CISA: Turn on MFA
- NIST: SP 800-63B, Authentication and authenticator management
- FTC Consumer Advice: Credit freezes and fraud alerts
- CFPB: What is a credit freeze or security freeze on my credit report?
- LII: 15 U.S.C. 1681c-1, Identity theft prevention; fraud alerts and active duty alerts
- FTC Consumer Advice: Free credit reports
- IRS: Get an identity protection PIN
- FTC: Data breach response, a guide for business
- FTC IdentityTheft.gov: Data breach steps
- FTC Consumer Advice: What to know about identity theft
- FBI Internet Crime Complaint Center: FAQ
Comments
No comments yet. Start the conversation below.